Security · Risk · Digital assets

Know where you stand. Fix what matters first.

Security and risk work for software, fintech and digital-asset companies in Latin America. Senior and hands-on: the person you talk to does the work.

  • Fixed fees
  • English or Spanish
  • Read-only access

Sound familiar?

Security usually stays invisible until someone asks.

  1. A customer sent a security questionnaire and nobody knows who should answer it.
  2. A prospect asked for SOC 2 or ISO 27001 before signing.
  3. Someone clicked the wrong link, and it became clear nobody owns security.
  4. Due diligence for a funding round or an acquisition is coming up.
  5. You hold client funds or keys, and regulators are starting to ask how you protect them.

Services

Three ways we help.

01

Security Baseline Assessment

A fixed-scope review of the essentials: accounts and access, email, laptops, cloud and code, data and backups, vendors and policies. Measured against CIS Controls and NIST CSF.

Best when
You have 10 to 150 people and nobody owns security full time.
You get
Findings ranked by risk and effort, a 30/60/90-day roadmap, a starter policy set and a readout with your leadership.
Timeline
Three weeks.
02

SOC 2 and ISO 27001 readiness

We map where you are against the standard, close the gaps with your team and prepare the evidence an auditor will ask for.

Best when
A customer or prospect has asked for a report or a certificate.
You get
A gap assessment, a remediation plan, policies and evidence, and help choosing an auditor.
Note
We prepare you. An independent, accredited auditor certifies you.
03

Digital-asset security and risk

Security and risk reviews for exchanges, brokers, stablecoin and payment companies: key management, custody and withdrawal approvals, third-party risk, and readiness for regulatory reviews in the region.

Best when
You hold client assets, or you are preparing for a licence or an audit.
You get
A control review, a risk register, a prioritised remediation plan and a board-ready summary.

Need help after the review? We stay on for guided remediation, and coordinate implementation and penetration testing through vetted specialists. One point of contact, one contract.

Free quick scan

How does your domain look from the outside?

A one-minute check of what anyone can see in public DNS: email spoofing protection, domain signing and certificate controls. Passive and read-only. We never touch your systems.

How we work

A baseline in three weeks, about three hours of your team's time.

  1. Week 1

    Kickoff

    A short call and a questionnaire, so we understand how your company actually works.

  2. Week 2

    Review

    Interviews and walkthroughs by screen-share or read-only access. Nothing changes in your systems.

  3. Week 3

    Results

    Findings, roadmap and policies, walked through with your leadership in a one-hour readout.

What you do

  • Answer a short questionnaire.
  • Share your screen or give read-only access.
  • Join the readout.

What we do

  • Run the interviews and review configurations, with AI-assisted checks.
  • Write every finding in plain language.
  • Rank each fix by risk and effort.
  • Draft the policies your customers will ask for.

Principles

How we keep it simple.

Fixed fee, agreed upfront.

No hourly billing and no surprises.

The person you talk to does the work.

No hand-off to a junior team after the sales call.

We don't change your systems.

Read-only access or screen-share, and an NDA before kickoff.

We never audit what we built.

Independence, for when your own auditor asks.

AI-assisted, human-verified.

Our tooling runs the repetitive checks. Every finding is reviewed and signed off by a person.

Your data stays yours.

We work from what you share, keep it only for the engagement and delete it at the end.

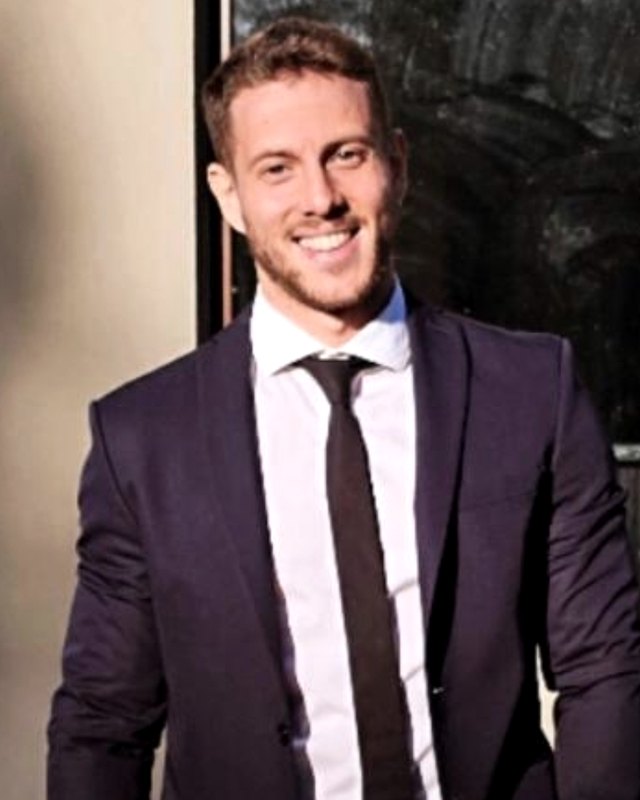
Nicolás Guillén

Who leads the work

Nicolás Guillén

More than eight years in security governance and risk, on the side of security that auditors, regulators and enterprise customers check.

  • EY. IT audit, SOX and business continuity work for banks and large companies.
  • Unilever. Business information security officer for South Latin America.
  • Buenbit. ISO 27001 and GDPR alignment at a crypto exchange regulated in Gibraltar.
  • Mountain Protocol. Led a SOC 2 Type II program end to end, and the wind-down of a regulated stablecoin.

Engagements run in English or Spanish.

FAQ

Questions we hear often.

How much does it cost?

Every engagement has a fixed fee, agreed after a 30-minute scoping call. A security baseline for a team of 10 to 150 people usually falls between USD 1,200 and 4,000, depending on size and how many systems are in scope.

Do you need access to our systems?

Only read-only access or a screen-share. We never change anything in your environment, and we sign an NDA before kickoff.

Do you fix the issues too?

The roadmap is written so your team can run it. If you want help, we stay on for guided remediation and coordinate implementation and penetration testing through vetted specialists, under one contract.

Can you certify us for SOC 2 or ISO 27001?

No. Reports and certificates are issued by independent, accredited auditors. We get you ready for them, and we never audit work we designed.

Do you work with crypto and stablecoin companies?

Yes. Our lead has run security and compliance programs at a regulated crypto exchange and at a regulated stablecoin issuer.

Where are you based?

We work remotely with clients across Latin America, the US and Europe, in English or Spanish.
Contact

Tell us what's on your plate.

We reply within one business day.

Book a 30-minute call

Or write to hello@quorantsecurity.com

What do you need?